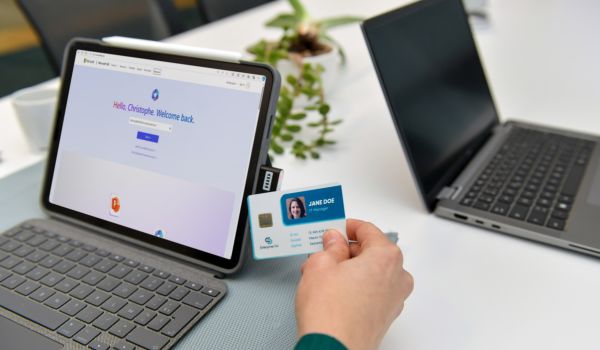
HID Introduces Enterprise Attestation for Passkey Governance
New FIDO-based capabilities allow organizations to verify device provenance during registration without impacting the end-user login experience.
- By Jesse Jacobs
- May 01, 2026
HID has launched Enterprise Attestation within its FIDO authenticator portfolio, a move designed to give organizations stricter control over credential registration. The new capability, integrated into the company’s smart cards and security keys, allows security teams to enforce policies that ensure only company-issued devices can be used to create passkeys.
While passkeys have become a primary defense against phishing, many enterprises remain concerned about the lack of visibility into device origin. Without attestation, organizations often cannot distinguish between a managed hardware security key and an employee-registered personal device. The Enterprise Attestation feature bridges this gap by verifying the authenticity of the device at the moment of enrollment.
The technology is built into HID’s Crescendo line of authenticators. When a user attempts to register a passkey, the system checks for a digital certificate tied to a known, company-issued device. If the device cannot provide valid attestation data, the enrollment is automatically blocked. This process occurs within existing application workflows, requiring no additional steps or changes for the employee.
This standards-based approach follows the FIDO Alliance’s WebAuthn and Client to Authenticator Protocol specifications. By adhering to these global standards, organizations can implement device governance without relying on proprietary authentication flows or risking vendor lock-in.
The capability is specifically aimed at highly regulated sectors, including financial services, healthcare and critical infrastructure. These industries face increasing pressure to meet auditability and device provenance requirements under frameworks such as the European Union’s NIS2 Directive and the Digital Operational Resilience Act.
By providing a verifiable record of every device granted access, the solution supports zero-trust mandates while maintaining a seamless user experience. The updated authenticators are currently available for global deployment and are compatible with identity platforms such as PingOne.